Every business relies on its website to attract customers, process transactions, and support day-to-day operations. At the same time, that website has become one of the most attractive targets for cybercriminals. New landing pages, cloud services, APIs, third-party plugins, and marketing tools are added so frequently that it’s easy to lose track of what’s actually exposed to the internet.
That’s where website attack surface management makes a difference. Instead of waiting for a vulnerability scan to uncover problems weeks later, it continuously looks at your digital presence from an attacker’s perspective. The result is better visibility, faster response times, and fewer opportunities for cybercriminals to exploit overlooked weaknesses.
What Is Website Attack Surface Management?
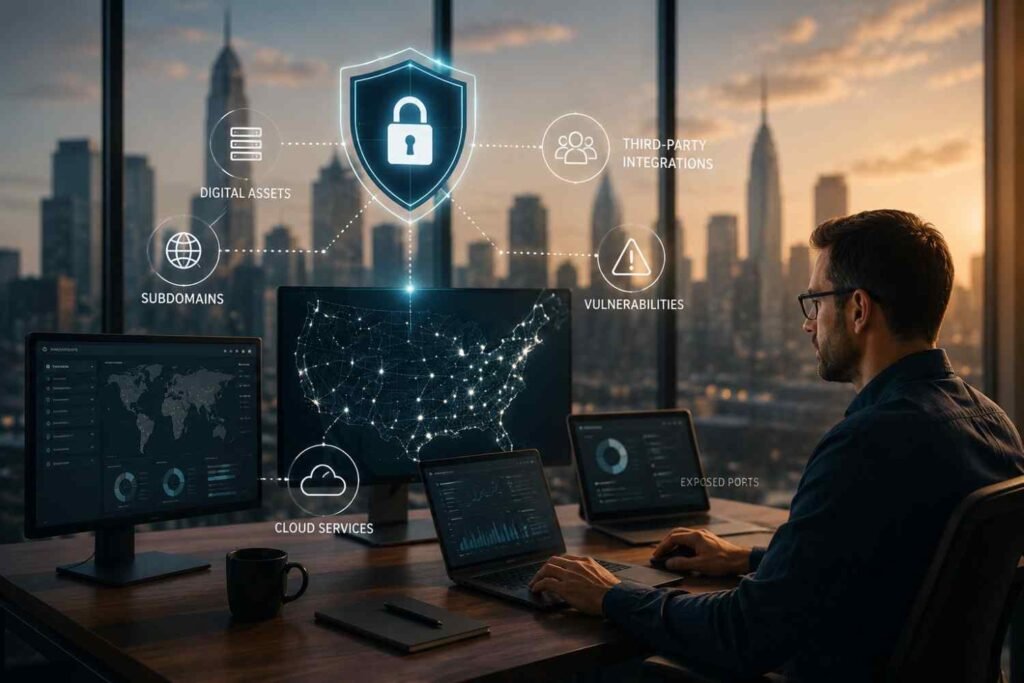
Website attack surface management is the continuous process of discovering, monitoring, and reducing every internet-facing asset that could become an entry point for attackers. Rather than focusing only on systems already listed in an asset inventory, it searches for everything connected to your organization—including forgotten subdomains, outdated applications, exposed APIs, cloud resources, and third-party services.
Unlike traditional security assessments that happen once every few months, attack surface management operates continuously. As your website evolves, so does your attack surface. New deployments, software updates, and infrastructure changes can introduce risks overnight, making ongoing visibility essential.
This proactive approach allows security teams to identify exposures before they become security incidents, strengthening an organization’s overall security posture.
Why Modern Websites Face More Cybersecurity Risks Than Ever
Today’s websites are far more complex than they were just a few years ago. A single website may connect with payment gateways, customer support platforms, analytics software, content delivery networks, and multiple cloud services.
While these integrations improve user experience, they also expand the digital attack surface.
Some of the most common reasons attack surfaces continue to grow include:
-
Cloud infrastructure expanding faster than documentation
-
Third-party applications with broad permissions
-
Public APIs that aren’t regularly reviewed
-
Temporary development environments left online
-
Shadow IT created outside approved security processes
-
Forgotten subdomains and legacy websites
Every additional asset increases the number of potential attack vectors. Without continuous asset discovery and monitoring, security teams may not even realize these exposures exist until they’re exploited.
How Website Attack Surface Management Helps Reduce Cybersecurity Risks
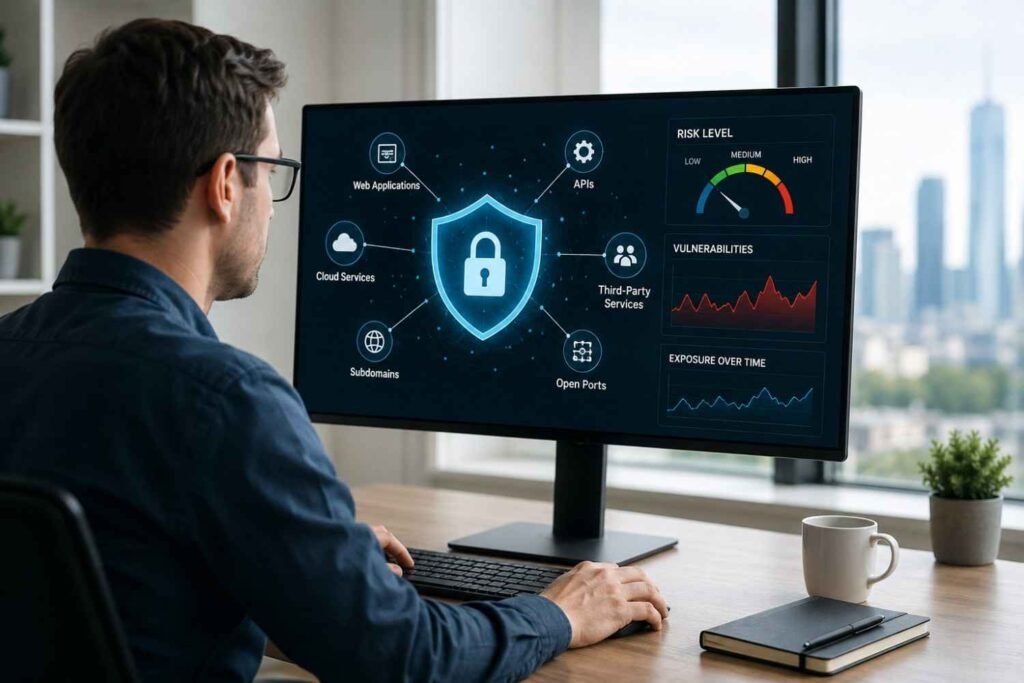
Discovers Unknown Internet-Facing Assets
One of the biggest cybersecurity challenges isn’t protecting known assets—it’s finding the ones nobody remembers.
Organizations often accumulate forgotten microsites, abandoned marketing pages, testing environments, and unused domains over time. These assets frequently miss security updates, making them attractive targets.
Website attack surface management continuously discovers internet-facing assets so security teams maintain an accurate asset inventory instead of relying on outdated documentation.
Detects Vulnerabilities Continuously
Traditional vulnerability scanning often follows scheduled assessments. Unfortunately, attackers don’t work on quarterly timelines.
Continuous attack surface monitoring identifies newly exposed services, outdated software, expired SSL certificates, open ports, and other security weaknesses as they appear.
Instead of reacting after a breach, organizations can remediate issues while the risk is still manageable.
Identifies Configuration Errors Early
Many cyber incidents aren’t caused by sophisticated hacking techniques. They’re caused by simple configuration mistakes.
Examples include:
-
Public cloud storage buckets
-
Default administrative credentials
-
Weak access controls
-
Exposed development environments
-
Incorrect DNS configurations
Website attack surface management continuously monitors these assets, helping teams correct human errors before attackers discover them.
Prioritizes the Most Critical Risks
Security teams often deal with hundreds—or even thousands—of alerts every week. Treating every issue with the same urgency isn’t practical.
Modern attack surface management platforms combine asset discovery with threat intelligence and risk assessment to prioritize vulnerabilities based on their likelihood of exploitation.
Instead of spending valuable time fixing low-impact issues first, teams can focus on vulnerabilities that pose the greatest business risk.
Strengthens Third-Party Risk Management
Very few websites operate independently today.
External widgets, plugins, JavaScript libraries, payment processors, customer chat platforms, and marketing tools all become part of a website’s security ecosystem.
If one of these third-party components becomes compromised, attackers may gain an unexpected entry point.
Website attack surface management continuously evaluates these external dependencies, helping organizations reduce supply chain risks while maintaining stronger visibility across their digital footprint.
Common Security Gaps Website Attack Surface Management Can Detect
Many organizations are surprised by what they discover during their first attack surface analysis. Common exposures include:
-
Forgotten subdomains still accessible online
-
Publicly exposed admin portals
-
Expired SSL certificates
-
Open ports with unnecessary services
-
Unmanaged cloud resources
-
Legacy web applications
-
Exposed APIs
-
Test environments accidentally left public
-
Misconfigured storage services
-
Unused DNS records
Finding these assets before attackers do significantly reduces cybersecurity risk and improves overall security posture.
If your organization is also reviewing how to protect your website from malware attacks, attack surface management provides valuable visibility by uncovering overlooked assets and security gaps before they become easy targets for malicious software.
Best Practices for Effective Website Attack Surface Management
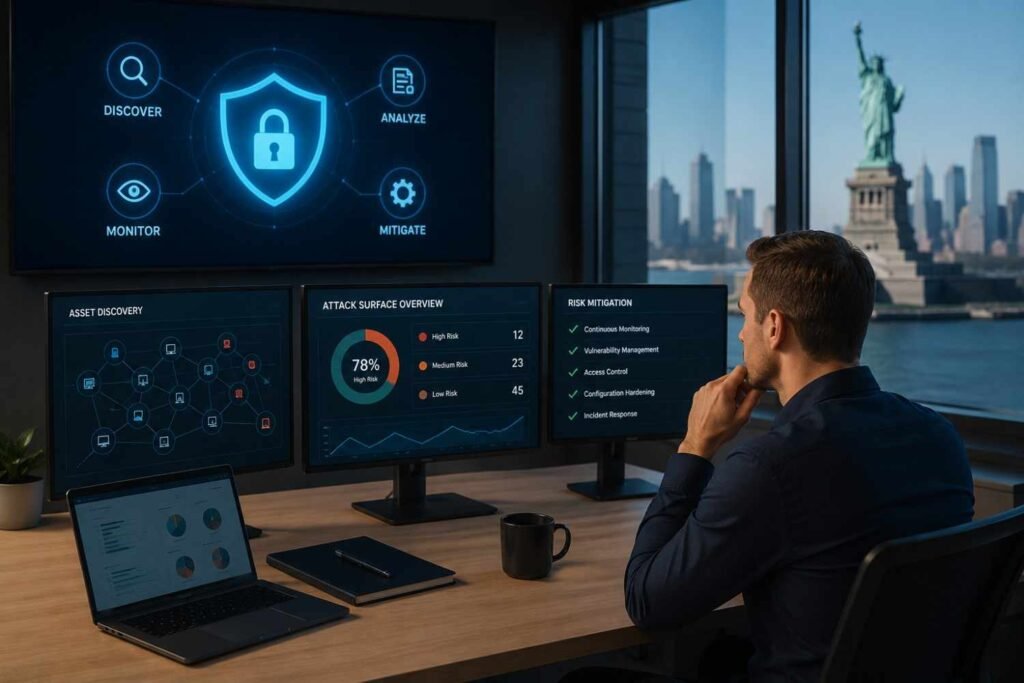
While every organization has unique security needs, these practices consistently improve results:
-
Maintain a continuously updated asset inventory.
-
Monitor internet-facing assets in real time.
-
Review cloud infrastructure regularly for misconfigurations.
-
Remove unused domains, applications, and services.
-
Prioritize remediation using risk-based intelligence.
-
Monitor third-party integrations and software dependencies.
-
Strengthen patch management processes.
-
Regularly validate security controls after infrastructure changes.