A secure website starts long before deployment. I believe developers should treat security as an essential part of building applications, not something to fix after discovering a vulnerability.
Following website security best practices for developers helps protect sensitive customer information, prevent cyberattacks, and reduce costly security failures. Whether you’re building an e-commerce platform, business website, or cloud-based application, secure development protects both users and organizations.
In this guide, I’ll explain practical security measures, common website vulnerabilities, and effective ways to protect modern web applications.
Why Is Website Security Important for Developers?
Websites regularly process login credentials, payment information, and personal data. Weak security controls can expose this information through unauthorized access, malicious scripts, or compromised software.
For American businesses, security failures may also trigger breach notification obligations under applicable state laws. Organizations handling regulated information may face additional requirements.
The OWASP Top 10:2025 identifies broken access control, security misconfiguration, and software supply chain failures among major web application risks.
Developers should address these threats throughout the software development lifecycle.
How Can Developers Prevent SQL Injection and XSS Attacks?
Input validation and secure data handling are essential secure coding practices for developers.
Validate and Sanitize User Input
Applications should treat incoming data as untrusted, whether it comes from forms, URLs, APIs, or uploaded files.
Perform server-side validation against expected formats, lengths, types, and values. Apply appropriate sanitization when handling permitted content, but never depend on sanitization alone to prevent injection.
For command injection and directory traversal prevention, use safe application APIs, restrict file paths, and avoid passing untrusted input into operating system commands.
Prevent SQL Injection With Parameterized Queries
SQL injection occurs when attackers manipulate database queries through improperly handled input.
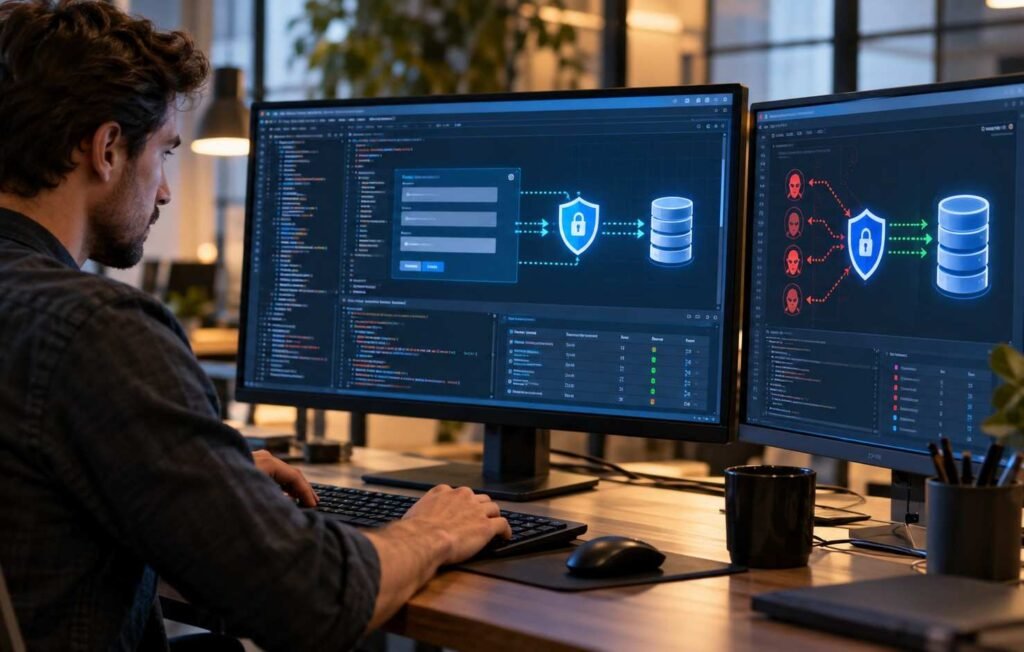
Developers should use prepared statements, parameterized queries, or safely configured object-relational mapping tools instead of combining user input directly with SQL commands.
These approaches separate user data from query instructions.
Stop Cross-Site Scripting With Output Encoding
Cross-site scripting (XSS) allows attackers to inject malicious browser-executable content into vulnerable pages.
Use context-specific output encoding, safe DOM operations, and trusted framework rendering methods.
For example, HTML text encoding converts special characters into safe representations rather than allowing browsers to interpret them as executable markup.
How Can Developers Secure Authentication and User Access?
Authentication and authorization are central to web application security best practices.
Use MFA, Passkeys, and Secure Password Storage
Multifactor authentication provides additional protection when passwords are compromised.
Developers should consider passkeys, phishing-resistant authentication, and centralized identity systems using OpenID Connect or SAML where appropriate.
Never store passwords as plain text. Use dedicated password-hashing algorithms such as Argon2id or appropriately configured bcrypt.
Protect Sessions and Apply Least Privilege
Configure authentication cookies with HttpOnly, Secure, and appropriate SameSite attributes.
Regenerate session identifiers after login, expire inactive sessions, and invalidate sessions during logout.
Apply the principle of least privilege so users and services receive only necessary permissions.
Role-based access control helps organize permissions, while server-side object-level checks prevent insecure direct object reference vulnerabilities.
Use Data Transfer Objects (DTOs) or explicit response schemas to avoid exposing confidential database fields through APIs.
How Can Developers Secure Servers and Website Infrastructure?
A website security checklist must include both application code and infrastructure.
Enable HTTPS, TLS, and Security Headers
HTTPS uses Transport Layer Security to encrypt browser-server communication.
Use valid TLS certificates and modern configurations. Enable HTTP Strict Transport Security (HSTS) where appropriate.
Configure Content Security Policy (CSP) to restrict resource loading and reduce certain injection risks. The frame-ancestors directive helps prevent unauthorized framing.
Additional headers, including X-Content-Type-Options: nosniff, strengthen browser security.
Add Rate Limiting and Web Application Firewalls
Rate limiting helps restrict excessive login attempts, abusive API requests, and automated attacks.
Deploy a Web Application Firewall (WAF) to filter suspicious HTTP traffic and provide additional protection against common attack patterns.
For distributed denial-of-service attacks, combine application controls with appropriate network and edge protections.
Neither rate limiting nor a WAF replaces secure coding.
Secure File Uploads
File upload functionality can introduce malware, unauthorized file access, and code execution risks.
Validate file extensions and actual content types, enforce file-size limits, and generate safe filenames.
Store uploads outside executable application directories, restrict access, and scan files for malware when appropriate.
How Can Developers Protect APIs, Databases, and Secrets?
Secure API development requires authentication, authorization, input validation, and controlled access to sensitive resources.
Never expose API credentials in frontend code. Apply request limits and verify authorization for every protected endpoint.
Database accounts should follow least-privilege permissions. Protect sensitive records through appropriate encryption, access restrictions, and reliable backups.
For secrets management, store API keys, database passwords, and encryption keys outside source repositories.
Use dedicated solutions such as HashiCorp Vault or managed cloud secret managers. Restrict access and rotate compromised credentials promptly.
How Can Developers Integrate Security Into CI/CD?
Security testing should continue throughout development rather than becoming a final deployment task.
Static Application Security Testing (SAST) identifies potential weaknesses in source code. Dynamic Application Security Testing (DAST) examines running applications, while Software Composition Analysis (SCA) detects vulnerable dependencies.
Tools such as OWASP ZAP, Semgrep, and Snyk support different parts of this process.
Integrate automated checks into CI/CD pipelines, review dependency updates, protect build credentials, and restrict pipeline permissions.
Dependency lockfiles and software bills of materials can improve supply chain visibility.
What Should Developers Check Before Launching a Website?
Before deployment, I recommend verifying HTTPS, authentication, server-side authorization, secure cookies, database protection, security headers, file uploads, and dependency updates.
Confirm that secrets remain protected and sensitive error details do not appear publicly.
Configure security logging, suspicious activity alerts, and appropriate monitoring. Test database backups and incident recovery procedures before relying on them.
These checks support a safer launch, but continuous vulnerability management remains essential.
Frequently Asked Questions (FAQs)
1. What Are the Most Important Website Security Best Practices for Developers?
The most important measures include secure authentication, least-privilege authorization, HTTPS, input validation, SQL injection prevention, XSS protection, dependency updates, and continuous security testing.
2. How Often Should Developers Test Website Security?
Developers should perform automated checks during development and before deployment. Additional reviews are necessary after major changes, security advisories, or significant infrastructure updates.
3. What Are the Best Website Security Testing Tools?
OWASP ZAP and Burp Suite support dynamic security testing. Semgrep helps analyze source code, while Snyk supports dependency vulnerability detection. Different tools serve different testing requirements.
4. Is HTTPS Enough to Make a Website Secure?
No. HTTPS encrypts transmitted information but cannot prevent insecure database queries, broken permissions, malicious uploads, or compromised dependencies. Effective security requires multiple protective layers.
Final Thoughts: Make Secure Development a Daily Practice
I believe successful website security depends on consistent development decisions rather than one-time security fixes.
By following OWASP guidance, protecting authentication systems, validating data, securing infrastructure, and continuously testing applications, developers can reduce exposure to common cyber threats.
For businesses managing customer information, these practices support stronger reliability, regulatory readiness, and user confidence. Incorporating a web performance optimization checklist alongside security best practices can also help developers maintain fast, reliable, and secure websites without compromising user experience.
The best approach is simple: build security into every stage of development, monitor applications after launch, and improve protections as new threats emerge.