Automated botnets hit my server logs with over 80,000 bad authentication requests in a single evening, all targeting /wp-login.php. Knowing how to secure website admin login against brute force attempts is the difference between a resilient portal and a catastrophic database compromise.
A strong password alone does not stop distributed clusters executing dictionary attacks and credential stuffing rounds. Modern attackers rotate residential proxies, bypass traditional lockouts, and exhaust underlying database connections until a website drops.
I manage multi-site web assets, and I treat authentication paths as critical attack surfaces. Hardening that portal requires a strict defense-in-depth model that merges application policies with edge-network controls. Integrating regular reviews with website vulnerability scanner tools keeps weak endpoints exposed to light before attackers exploit them.
The Reality of Modern Automated Login Attacks
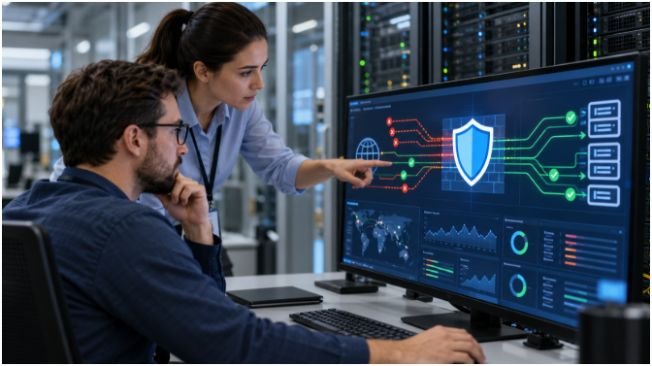
A brute force attempt is no longer just one compromised terminal trying hundreds of combinations against a single username. Threat actors deploy distributed password spraying across thousands of clean residential IP addresses. They target common administrative usernames to evade primitive per-IP rate limiters.
Distributed Botnet (Rotating IPs)
│
▼
[ Edge Network / WAF ] ──► (Drops Volumetric Floods & Known Bad Proxies)
│
▼
[ Origin Server / Nginx ] ──► (Enforces IP Whitelists & Memory Rate Buckets)
│
▼
[ Application Layer ] ──► (Requires Passkey/MFA & Generic Error Messages)
Why Complex Passwords Fail on Their Own
A 20-character password helps against offline hash cracking, but it does little against brute-force resource starvation. Attackers hit unthrottled login forms, forcing the application framework to execute expensive cryptographic hashing algorithms like Argon2 or bcrypt for every invalid guess.
According to authentication benchmarks outlined by the OWASP Automated Threat Handbook, uncontrolled login queries easily degrade back-end CPU performance. The server crashes under the computational strain of hashing fake passwords before an attacker even guesses correctly.
Application-Level Controls to Harden Your Login Entryway
Your core application code provides the initial perimeter against casual scanners and credential lists.
Enforcing Phishing-Resistant MFA
Multi-Factor Authentication (MFA) remains your most reliable application safeguard. If a password leaks, secondary token checks stop unauthorized entry.
I avoid SMS-based two-factor authentication on administrative accounts. Attackers routinely bypass SMS verification through SIM-swapping attacks and SS7 exploitation. Instead, I mandate hardware security keys (FIDO2/WebAuthn) or time-based one-time passwords (TOTP) through dedicated authenticator apps, aligning with NIST SP 800-63B guidelines.
URL Masking and Error Sanitisation
Standard admin entry points like /wp-admin, /administrator, or /user/login attract continuous background traffic. Changing this endpoint to a unique, non-obvious slug eliminates automated noise from off-the-shelf bots.
Simultaneously, sanitize all responses on authentication failures. Default CMS behavior often specifies whether a username exists:
- Vulnerable output: “Password for user ‘alex’ is incorrect.”
- Hardened output: “Invalid credentials.”
Revealing that a username is valid hands the attacker half of the required authentication pair. Suppress descriptive authentication errors to stop automated username enumeration.
Server and Network Edge Protections
Securing the PHP or Node.js runtime is insufficient if your web server still processes every malicious request. Offload this enforcement to your web server configurations and edge proxies.
Nginx and Apache Rate-Limiting Rules
Throttling connection frequency shields processing memory. Nginx handles this through shared memory zones that track incoming connection states.
Nginx
# Define the zone in your http {} context
limit_req_zone $binary_remote_addr zone=admin_limit:10m rate=5r/m;
limit_req_status 429;
# Apply within your administrative server {} or location {} block
location = /custom-login-page.php {
limit_req zone=admin_limit burst=3 nodelay;
include fastcgi_params;
fastcgi_pass unix:/var/run/php/php8.2-fpm.sock;
}
This configuration restricts individual IP addresses to five requests per minute. Bursts of up to three requests process instantly, while excess requests receive an immediate HTTP 429 (Too Many Requests) without reaching your database.
For Apache servers running mod_authz_core, restrict administrative directories to trusted management subnets:
Apache
<Files “custom-login-page.php”>
<RequireAny>
Require ip 198.51.100.24
Require ip 203.0.113.0/24
</RequireAny>
</Files>
IP Whitelisting and the Origin Leak Problem
Restricting admin login endpoints strictly to trusted internal corporate IPs or secure VPNs blocks untrusted access attempts outright. However, an edge firewall like Cloudflare Application Security only protects you if attackers are forced through it.
During security audits, I frequently observe a dangerous loophole: administrators proxy traffic through an edge Web Application Firewall (WAF), but their origin server remains exposed to the public internet on ports 80 and 443. Attackers discover the origin IP through historical DNS registries or MX records, bypass edge WAF protections entirely, and brute force the web server directly.
Ensure your origin firewall rules (using ufw or iptables) strictly reject direct HTTP/S connections from any source other than your proxy’s designated IP blocks. Document these procedures inside your organization’s broader website security checklist to prevent configuration oversights during infrastructure migrations.
Automated Defense with Fail2ban and Behavioral Challenge Shields
When unauthorized connection attempts slip past the perimeter, automated log parsing mitigates persistent attacks. I deploy fail2ban to monitor server access logs and dynamically drop hostile traffic at the operating system firewall level.
Ini, TOML
[admin-auth]
enabled = true
port = http,https
filter = admin-auth-filter
logpath = /var/log/nginx/access.log
maxretry = 4
findtime = 600
bantime = 86400
This rule scans for repeated failed POST requests to the login endpoint. If an IP triggers four failures within ten minutes, the host drops all incoming traffic from that source at the kernel level for 24 hours.
Pairing host-level log parsers with managed challenge systems like Cloudflare Turnstile blocks automated scripts without introducing friction for legitimate administrators. Turnstile evaluates visitor interaction silently, verifying browser telemetry without forcing team members to complete image puzzles. This setup minimizes automated credential attacks before they touch internal server assets.
Frequently Asked Questions
1. Does changing the admin URL fully stop brute force attacks?
No, security through obscurity only blocks automated default scanners; determined attackers locate custom endpoints through access logs, network sniffing, and directory brute-forcing.
2. What is the safest lockout threshold for failed administrative logins?
Lock accounts or apply aggressive rate limits after three to five consecutive failed attempts within a ten-minute window to balance security against unintentional staff lockouts.
3. Can brute force attacks succeed against passwordless passkey setups?
No, WebAuthn passkeys rely on public-key asymmetric cryptography, making dictionary-based password guessing mathematically impossible.
4. Why are SMS-based two-factor codes discouraged for administrator portals?
SMS messages lack end-to-end encryption and remain vulnerable to SIM-swap fraud, mobile carrier interception, and social engineering.
Stop Guessing, Start Dropping
Securing your administrative portal against brute force is not about writing complex password requirements that your staff forgets. It is about shrinking your attack surface until automated attempts bounce off the network perimeter without burning server resources.
Audit your origin IP exposure, replace SMS verification with hardware-backed passkeys, and enforce strict server-side throttling today.