Every browser flags an unencrypted connection within milliseconds. When you run a site on raw HTTP, visitors bounce immediately, search engines demote your rankings, and data passes across public networks in clear text. Knowing how to configure ssl tls certificates for website environments is a baseline operational requirement for anyone deploying web applications today.
I have spent years configuring production servers, debugging broken handshakes, and fixing botched migrations. A green padlock in the address bar is only step one. True security means eliminating obsolete protocols, ensuring certificates renew without human intervention, and maintaining strict transport integrity.
Pre-Flight Checklist: What You Need Before Touching the Server
Issuing a certificate requires proving legal control over the destination hostname. If the host infrastructure is unprepared, validation fails immediately.
DNS Propagation and Firewall Rules
Your domain must resolve directly to your public server IP before you initiate certificate issuance. Run dig +short yourdomain.com in your local terminal. If the returned A or AAAA records point to an old host, stop. Wait for DNS records to propagate.
Next, verify server ports. Web servers use port 80 for standard HTTP verification traffic and port 443 for TLS encrypted handshakes. Firewalls like UFW or AWS Security Groups must allow inbound connections on both:
Bash
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
sudo ufw reload
Blocking port 80 causes automated domain validation to drop instantly.
Selecting Between Manual CSR Issuance and Automated ACME
Commercial certificates from vendors like DigiCert or Sectigo require a manual Certificate Signing Request (CSR). These remain common for enterprise organizations requiring Extended Validation (EV) or Organization Validation (OV).
For almost every other use case, automated ACME via Let’s Encrypt is the superior option. Automated issuance eliminates human scheduling errors. Let’s Encrypt certificates expire every 90 days, forcing you to maintain a reliable renewal pipeline rather than scrambling through an emergency manual renewal every twelve months.
Method 1: The Modern Standard (Automated Let’s Encrypt via Certbot)
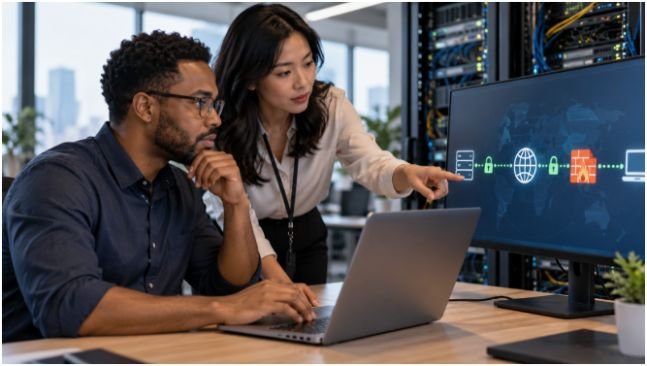
Automated provisioning handles domain verification, obtains the certificate payload, modifies configuration files, and restarts worker threads automatically.
Provisioning and Securing Nginx
On an Ubuntu or Debian distribution, install Certbot and its dedicated Nginx connector:
Bash
sudo apt update
sudo apt install certbot python3-certbot-nginx -y
Confirm your virtual host block at /etc/nginx/sites-available/yourdomain.com defines your domain accurately:
Nginx
server {
listen 80;
server_name yourdomain.com www.yourdomain.com;
root /var/www/html;
}
Run the automated installer:
Bash
sudo certbot –nginx -d yourdomain.com -d www.yourdomain.com
Certbot queries your server via an HTTP-01 challenge, receives the cryptographic response, installs the certificate bundle under /etc/letsencrypt/live/, and injects the necessary HTTPS redirect blocks automatically.
Provisioning and Securing Apache
The installation flow on Apache mirrors Nginx closely:
Bash
sudo apt update
sudo apt install certbot python3-certbot-apache -y
Ensure your configuration file within /etc/apache2/sites-available/ declares both ServerName yourdomain.com and ServerAlias [www.yourdomain.com](https://www.yourdomain.com). Run the utility:
Bash
sudo certbot –apache -d yourdomain.com -d www.yourdomain.com
Certbot builds an SSL-enabled clone of your virtual host configuration, modifies your .conf files, and enables Apache’s ssl module.
Validating Unattended Auto-Renewals
Certbot installs a systemd timer that runs twice daily to renew any certificates within 30 days of expiration. Never assume a cron task works without empirical proof. Run a simulation run immediately:
Bash
sudo certbot renew –dry-run
If the dry run finishes without outputting error tracebacks, your automation is operational.
Method 2: Manual Commercial Certificate Installation
If your compliance policies demand a paid commercial certificate, you must generate the cryptographic keypair on your server directly.
Generating Your Private Key and CSR with OpenSSL
Log into your target server via SSH. Execute the following OpenSSL command:
Bash
openssl req -new -newkey rsa:2048 -nodes -keyout yourdomain.key -out yourdomain.csr
- Store yourdomain.key in a secure location (such as /etc/ssl/private/) with file permissions locked to chmod 600. Never share or expose this file.
- When prompted for the Common Name (CN), type your exact domain name (yourdomain.com).
- Copy the generated .csr text and submit it to your certificate authority.
Building the Complete Chain Bundle Correctly
Once validated, your CA delivers two files: your leaf certificate (yourdomain.crt) and an intermediate CA bundle (intermediate.crt).
Nginx requires these combined into a single file. The ordering is critical:
Bash
cat yourdomain.crt intermediate.crt > fullchain.crt
Point your Nginx configuration directly to this merged bundle:
Nginx
server {
listen 443 ssl http2;
server_name yourdomain.com;
ssl_certificate /etc/ssl/certs/fullchain.crt;
ssl_certificate_key /etc/ssl/private/yourdomain.key;
}
Hardening Your Configuration Beyond the Green Padlock
Installing a certificate establishes an encrypted tunnel, but weak parameters leave your infrastructure exposed to downgrade exploits.
Enforcing Modern Ciphers and TLS 1.3
Deprecate legacy TLS versions. TLS 1.0 and 1.1 contain known protocol vulnerabilities. Follow the cryptographic baselines established by NIST Guidelines for TLS Implementations and Mozilla’s Intermediate Server Profile:
Nginx
ssl_protocols TLSv1.2 TLSv1.3;
ssl_prefer_server_ciphers off;
ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305;
This configuration stops downgrade attacks and forces fast, forward-secret handshakes.
Activating HTTP Strict Transport Security (HSTS)
Even with 301 redirects enabled, an attacker executing a man-in-the-middle attack can intercept that initial unencrypted HTTP handshake. Prevent this by serving an HSTS header:
Nginx
add_header Strict-Transport-Security “max-age=31536000; includeSubDomains” always;
This forces compliant browsers to interact exclusively over HTTPS for a full year. Keep in mind that securing traffic at the perimeter is only one layer of defense; pair this with robust application-level checks to stop cross site scripting attacks in web forms.
Two Costly Mistakes I Still Catch in Production Audits
1. Inverted Certificate Concatenation
The single most common bug I encounter during technical server audits involves the concatenation order of commercial certificates. If you run:
Bash
cat intermediate.crt yourdomain.crt > broken_chain.crt
Desktop browsers like Chrome or Firefox will often pass the connection because they cache root intermediate authorities locally. However, mobile browsers and programmatic API clients (like Python or cURL) will immediately fail with SSL_ERROR_UNKNOWN_CA_ALERT. Your leaf certificate must always reside at the absolute top of the combined file.
2. Silent Auto-Renewal Failures
Automated renewals fail silently when engineers configure reverse proxies without persistent webroot paths. If Certbot cannot write its temporary .well-known/acme-challenge/ token to disk, or if your firewall rules change, the certificate expires without warning.
Monitor your certificates using an external uptime monitor, and maintain active website malware removal workflows alongside server integrity scans.
Run your completed domain through the Qualys SSL Labs Engine to inspect your cipher curves, forward secrecy, and chain construction.
Frequently Asked Questions
1. Can I secure multiple domains with a single certificate?
Yes, using a Subject Alternative Name (SAN) certificate or a wildcard certificate (*.yourdomain.com).
2. What is the difference between SSL and TLS?
TLS is the modern, secure successor to SSL, though the industry still uses the terms interchangeably.
3. How often should I test my certificate renewals?
You should simulate renewals monthly using dry-run tests and verify automated alerts via monitoring tools.
4. Why does my browser still say “Not Secure” after installation?
This usually stems from mixed-content errors, where external images or scripts are fetched over unencrypted HTTP.
The Padlock Is Yours—Keep It Locked Down
Setting up an encrypted website is no longer a dark art or a manual annual chore. Once you understand the mechanics of key generation, automated ACME challenges, and chain validation, you can deploy rock-solid HTTPS across any web server in under ten minutes. Lock down your ports, automate your renewal timers, test your domain on SSL Labs, and never lose sleep over expired certificates again.